Compliance and security, proven with evidence.
Compliance, privacy, code, cloud and AI security on one read-only platform. License only the products you need, under one agreement.
Read-only cloud access · No agents to install · SaaS, dedicated or self-hosted
Compliance overview
Scored from live findings and your privacy programme
SOC 2
88%
7 of 8 controls passing
ISO 27001
86%
6 of 7 controls passing
GDPR
87%
13 of 15 requirements met
DPDP Act
88%
14 of 16 requirements met
Evidence trail
- Evidence pack signed for SOC 2just now
- Consent withdrawn and logged, DPDP Act6 min ago
- Erasure request closed, GDPR24 min ago
Open rights requests
10
Due in 7 days
2
Consent decisions, 30 days
32
Consent purposes
4
Frameworks built in
- SOC 2
- ISO 27001
- GDPR
- DPDP Act
- HIPAA
- PCI DSS
- NIST CSF
- FedRAMP
Six products. One platform.
Each product stands on its own and is licensed on its own. They share one connection, one inventory, one findings queue and one audit trail.
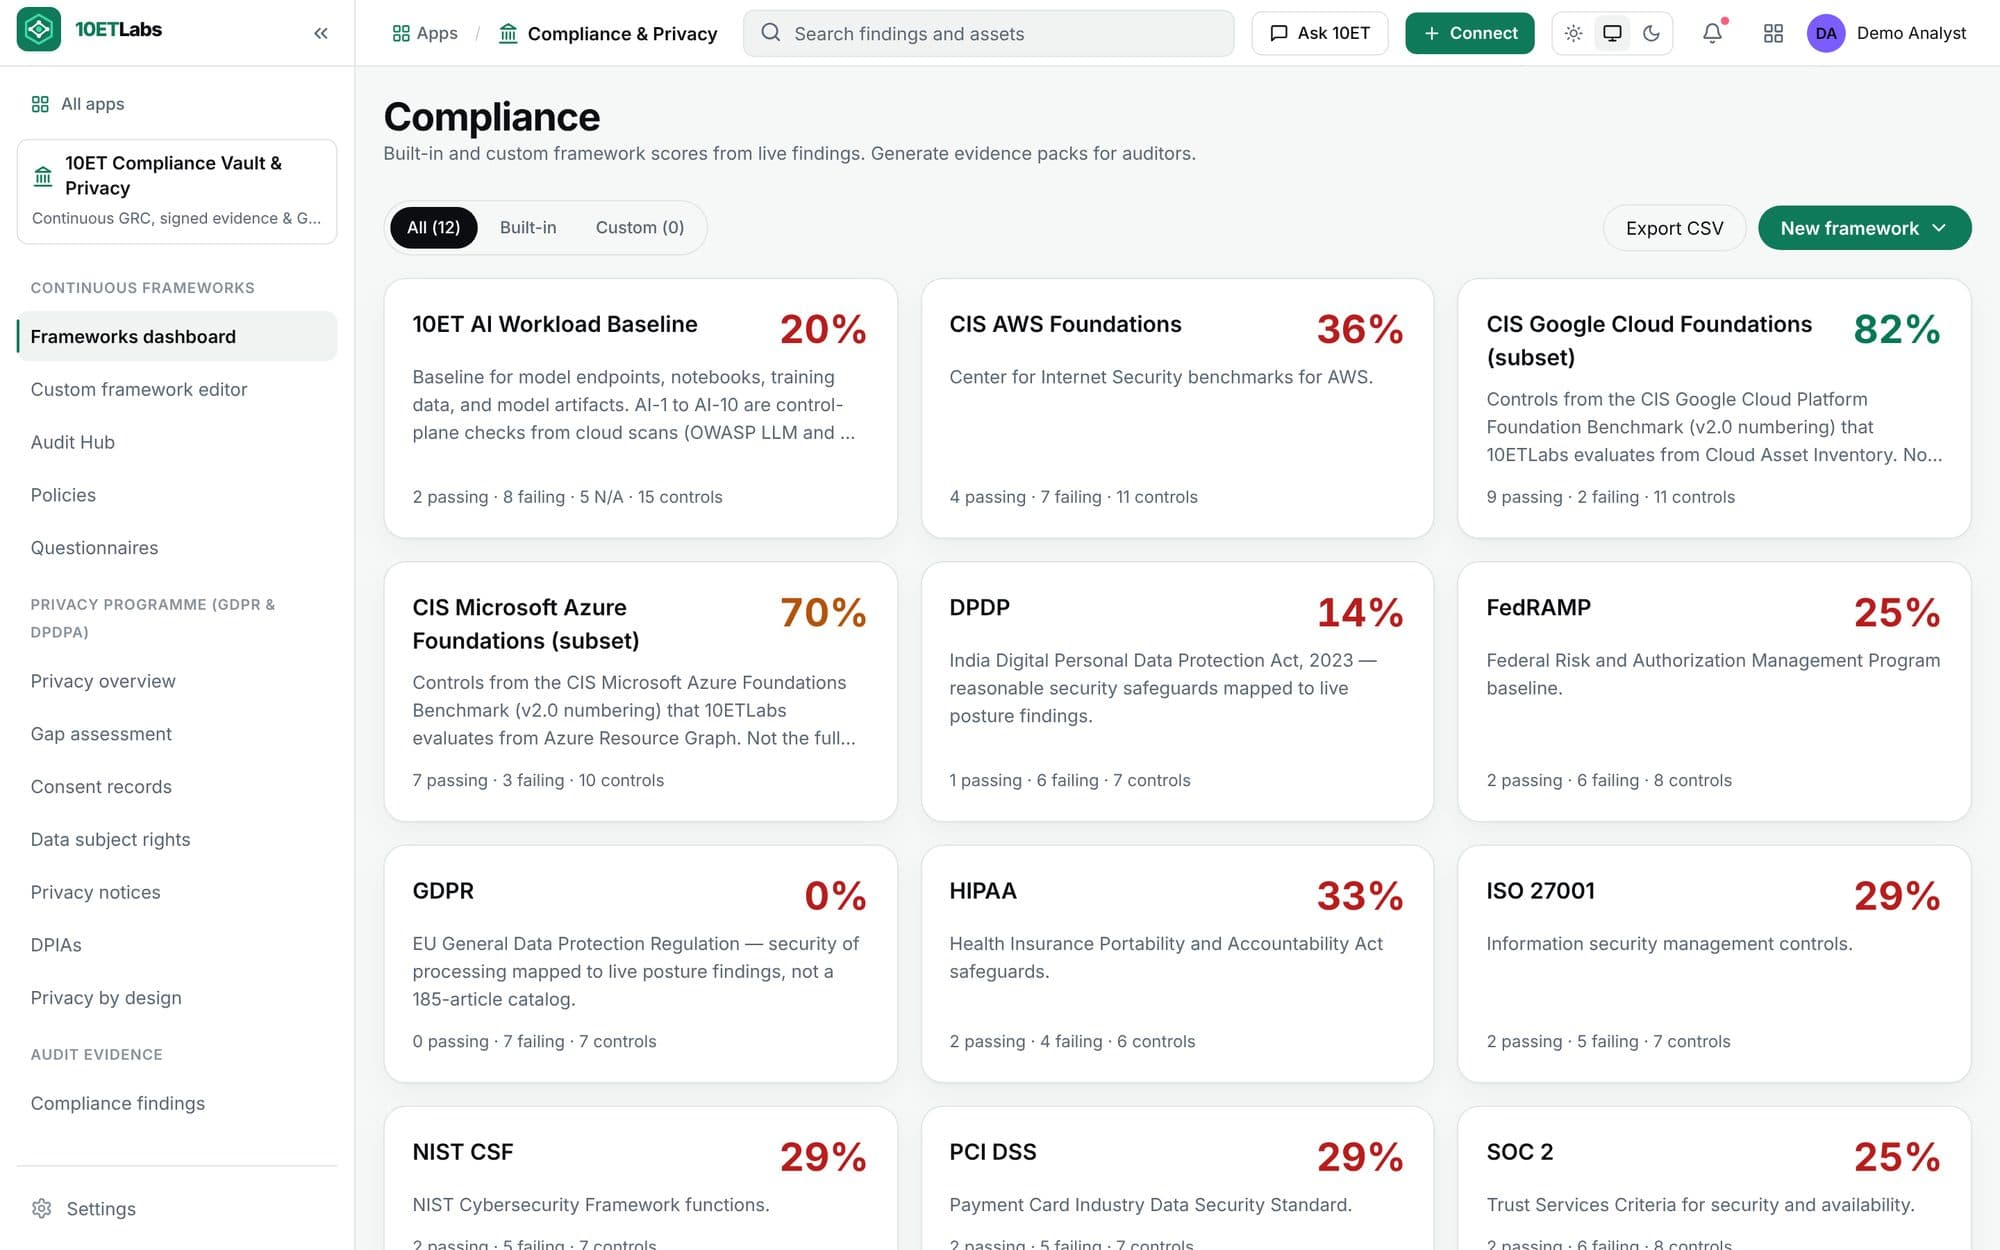
Compliance & Privacy
Continuous GRC evaluation, auditor-ready signed evidence packs, and a complete GDPR and DPDPA consent and rights programme in one product.
Learn moreCode Security
Application security and source control posture across GitHub, GitLab, Bitbucket and Azure DevOps.
Learn moreCloud Posture
Agentless multi-cloud visibility, CIS benchmarks and evidence-backed attack paths across AWS, Azure, GCP and Kubernetes.
Learn moreAI Shield
Security posture and prompt testing for the generative AI, LLMs and foundation models you run.
Learn moreDeepScan
In-account, agentless VM disk scanning for AWS EBS, Azure Disks and GCP Disks with no impact on the workload.
Learn moreRuntime Guard
Kubernetes runtime evidence and admission control that warns on or blocks risky deployments.
Learn more
- products on one platform
- 6
- compliance frameworks built in
- 12
- agents to install
- 0
- read-only role per cloud account
- 1
A closer look at each product
What each product does today, who it is built for, and what your team gets from it.
10ET Compliance Vault & Privacy
Continuous GRC evaluation, auditor-ready signed evidence packs, and a complete GDPR and DPDPA consent and rights programme in one product.
- Continuous GRC (12 frameworks)SOC 2, ISO 27001, HIPAA, PCI DSS, NIST CSF, FedRAMP and the AI baseline
- GDPR & DPDPA privacy programmeGap assessment, consent records, data subject rights deadlines, notices and DPIAs
- Ed25519-signed evidenceHash-chained evidence packs your auditor can verify offline
- Custom framework authoringYour own internal controls and manual attestations next to the standards
Built for
Head of GRC, Data Protection Officer
Replaces audit screenshots and spreadsheets, and keeps consent and rights requests on the record for the regulator.
From connection to evidence in three steps.
01
Connect read-only
Add one reader role per cloud account, or connect a repository. Nothing to install on a single host.
02
Assess and rank
Findings from every product land in one queue, ranked by exposure and mapped to the controls they affect.
03
Prove it with evidence
Framework scores move as you fix, and signed evidence packs go straight to your auditor.
One set of facts for everyone in the review
Every team works from the same inventory and the same findings queue, so nobody reconciles five tools before the meeting.
Compliance and privacy
Framework scores and DPDP and GDPR records move with the estate, with signed evidence your auditor can verify.
Learn moreSecurity operations
Start the week from the riskiest path to your data, not the newest alert from the loudest cloud.
Learn moreCloud platform
Prove coverage of every account from one read-only role, without installing agents on a single host.
Learn more
Built to pass your security review
Commitments the product enforces today. Your reviewers can check each one in a walkthrough.
Read-only by default
The cloud role you grant cannot change anything. Write access exists only if you deploy a separate role yourself.
Secrets stay sealed
Connection credentials are encrypted with AES-256-GCM. No screen or API returns them in plaintext, including to our operators.
Every access is audited
Sign-ins, role changes, connection changes and support sessions land in an audit log your admins can filter and export.
Evidence you can verify
Compliance evidence packs are hash-chained and Ed25519-signed, so an auditor can check them offline without trusting us.
For your security and legal reviewers
Available under NDA before you connect anything.
- Architecture & data-flow overview
- Subprocessor list
- DPA template
- Security questionnaire (CAIQ-lite)
Request them from security@10etlabs.com
Certifications
SOC 2 is in preparation and not yet audited. We show a badge here only once an auditor has issued it.
Full data inventory and disclosure policyIs 10ETLabs agentless?
Yes, for cloud connections. You grant a reader role, Kubernetes get/list, or a VPS token you already control. Nothing installs in the guest OS unless you choose the optional host sensor for VPS hosts, and nothing runs in your clusters unless you install the optional Kubernetes runtime sensor or admission webhook. Opt-in DeepScan is agentless too: it scans disk snapshots in your own account.
Do you write back to our clouds?
Not by default. Every connection is read-only. Fixes are code you review: findings for the top rules come with a generated Terraform, CloudFormation, Azure CLI / Bicep, gcloud or Kubernetes patch you copy, download, or (if you turn on the separate write opt-in for a source-control connection) receive as a pull request on a new branch. Only if you deploy a separate remediator role, with its own identity and only the exact write permissions of each supported fix, can an Owner or Admin approve one-click changes. Each one shows before and after, is confirmed by re-reading the resource, is fully audited, and can be rolled back where the change is reversible.
What data do you keep after a scan?
Asset metadata, findings, membership, encrypted connection secrets, and Ask 10ET chat history. Not disks, object bodies, or packet captures. The Trust center has the full inventory.
Can we run it in our own cloud?
Yes. The same product installs in your account with a Helm chart or on a single VM, with your Postgres and Redis. Your cloud metadata and the key that encrypts your credentials stay with you, and the license is checked offline with no phone-home. Ask 10ET stays off unless you add your own OpenAI key. See Run it in your cloud.
Can we self-serve checkout?
No. Billing is sales-led and production tenants are invite-only. Request a walkthrough and we will quote on your connected accounts.
Evaluate it on your own estate
Tell us which products your teams are evaluating. We set up a workspace with just those, on a read-only connection.