AI & ML teams
Ship models without leaving the door open
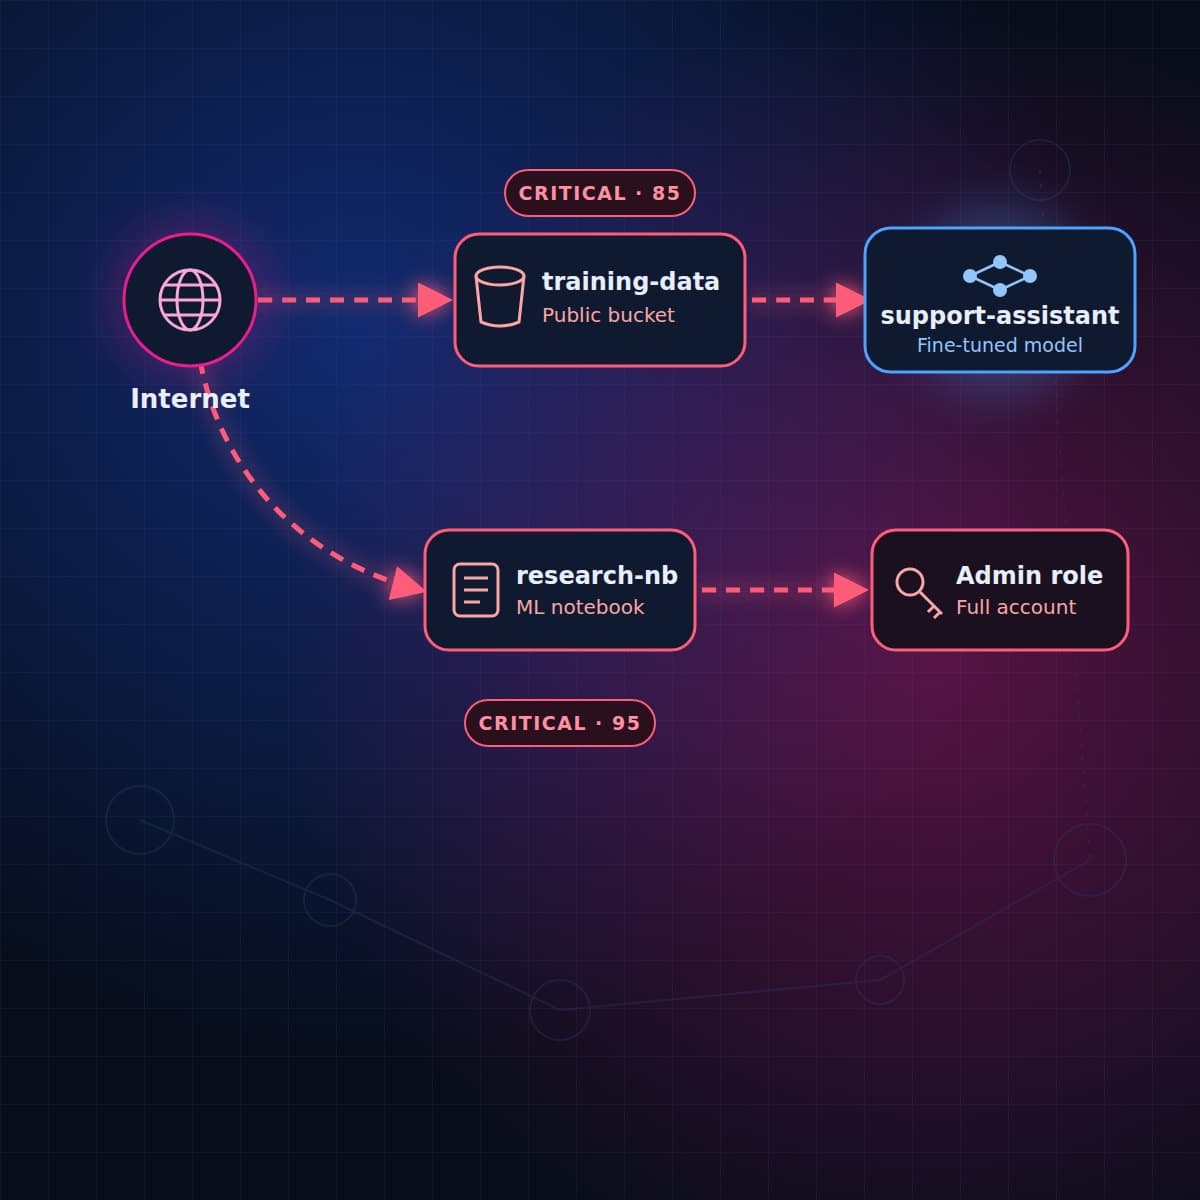
ML platform and security teams see the paths from the internet to model weights, training data, and captured inference data on AWS.
AI projects move fast and borrow broad roles and shared buckets to do it. 10ETLabs shows which notebooks, endpoints, and custom models are exposed, what data they touch, and which role they run as — so you can fix the few paths that matter without slowing the team down.
We read configuration only, never prompts or weights, and we never call your models. Prompt-injection tests run on your side with the 10et-ai-test CLI; you can upload just the verdicts.
AI & ML teams
Every exposed model, training bucket, and over-privileged notebook role on one ranked list.
A typical week
Before launch: check the model
Scan the account. A public bucket feeding the endpoint or an admin notebook role shows up as a path, not a hunch.
Weekly: watch the supply chain
New fine-tuned models, training buckets, and capture settings are re-linked on every scan. Paths close when the fix lands.
For audit: show the baseline
The 10ET AI Workload Baseline scores logging, guardrails, data exposure, and least privilege from live findings.
What this seat opens
AI estate · Attack paths · Compliance (AI baseline) · Findings
Other seats
Walk through the AI & ML teams seat
The agenda is on Request demo. This page stays the typical week.